
- player account
- identity
- KYC
- session management
Player Account Management Architecture for iGaming Platforms
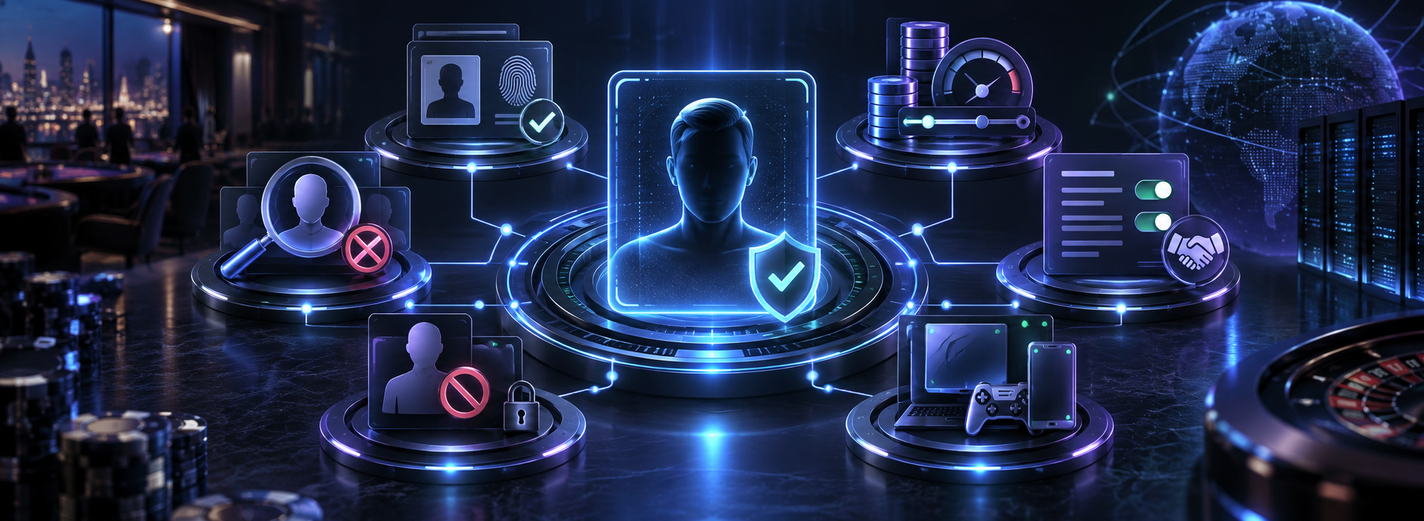
Design player accounts around explicit state and ownership: identity checks, restrictions, limits, consent, sessions, provider failures, and practical acceptance tests.
A player verifies their identity, then changes the details that were checked. A delayed provider callback arrives after the account has been restricted. A player activates self-exclusion in one browser while a game remains open in another. These cases expose why player account management is more than registration and a profile record.
Player account management (PAM) connects identity, account lifecycle, eligibility and the platform's other domains. Its architecture must explain which facts each component owns, how those facts authorise an action, and how a decision remains enforceable when requests and events arrive concurrently.
This guide is for product, engineering and operations teams designing or reviewing an iGaming platform. It provides a working state model, concrete transition examples and an acceptance checklist. The examples are design patterns to adapt to the operator's approved market and player-protection policies; they are not a universal regulatory specification.
1. Define the account boundary and the actions it controls
Start with the actions you need to control: create an account, authenticate, update identity details, deposit, start a game or place a bet, request a withdrawal, change a limit, and contact support. Define the conditions for each action separately. A single “active” flag cannot express all of them.
For example, blocking new gambling is a different decision from denying access to statements, support or a permitted funds-return process. Define those paths explicitly with the operator's responsible teams. Do not let a generic suspended-account check silently decide every financial and service outcome.
- PAM: owns stable account identifiers, profile changes and the account lifecycle. Specify the scope of identifiers across brands, operators and markets.
- Authentication: owns credentials, authentication factors and sessions. An authenticated session establishes a caller; it does not by itself establish permission to gamble.
- Verification: owns cases, submitted identity versions, evidence and decisions. A provider's response is input to that process, not authority to remove every account restriction.
- Player protection: owns applicable exclusions, limits and their effective scope. State which controls cover one account, several brands or a wider scheme.
- Wallet and payments: own financial postings and payment outcomes. PAM supplies eligibility and identity references rather than becoming a second balance ledger.
For an operator covered by Great Britain's LCCP condition 17.1.1, identity must be established before gambling. The condition also limits withdrawal-stage information requests that could reasonably have been made earlier, subject to other legal obligations. Confirm applicability; other markets need their own approved rules.
These boundaries should be explicit in casino platform development and payments and KYC integration. Choose storage and deployment boundaries after deciding ownership, consistency and failure behaviour. A well-separated module can be appropriate without becoming a separate network service.
2. Separate lifecycle, verification and restrictions
Model independent dimensions instead of an ever-growing status field. An account can be open, identity-verified and self-excluded at the same time. If these facts share one enum, a later “verified” update may accidentally overwrite the exclusion.
- Account lifecycle: registration pending, open, closure requested and closed are possible states. Define reopening separately instead of assuming that a new login reverses closure.
- Verification case: not started, submitted, pending, approved, declined and manual review describe the case. Store which identity data and policy version the decision covers; decide when reassessment is required.
- Restrictions: record each reason independently, including its source, effective time, scope and authorised removal path. One cleared reason must not clear unrelated restrictions.
- Limits: store the rule, measurement period, currency, time zone, effective schedule and authoritative usage. Separate a requested change from a change that is already effective.
- Consent and preferences: record the purpose, channel, notice version and grant or withdrawal history. Marketing preferences should not masquerade as gambling eligibility or a blanket legal basis for every use of data.
- Session state: track the session's creation, assurance, expiry and revocation independently from the business state of the account.
Compute action-specific eligibility from these facts under a versioned policy. Keep the decision reason understandable to operations and give the player an appropriate explanation without exposing sensitive fraud rules.
A derived “can play” flag may be useful for display or reporting. It should not become an independent writable truth that drifts away from exclusions, verification or limits. Name the owner of the authoritative decision and define how consumers detect stale information.
3. Trace registration through the first authorised action
Walk one journey from account creation to a permitted value-bearing action. The objective is to locate decisions and durable records, not to draw every service on a diagram.
- Registration: issue a stable account ID, validate the permitted uniqueness rules and record the accepted registration data. A repeated submission must not accidentally create two accounts.
- Identity submission: create a verification case tied to the account and an explicit identity-data version. Send only the information required by the provider contract.
- Provider response: authenticate the callback using the agreed mechanism, durably record its reference and map its result to the correct case. A successful HTTP response should acknowledge the handling the integration actually guarantees.
- Eligibility decision: evaluate the applicable verification outcome alongside current restrictions and policy. Approval of the case must not automatically reopen a closed or excluded account.
- Protected action: re-evaluate the required permissions at the service that accepts the deposit, bet or game request. Link the decision, account and financial operation with reviewable references.
- Operations view: show the current facts, decision reasons and unresolved work so support does not need to infer eligibility from a provider's dashboard.
Prevent races between checking eligibility and accepting the action. For controls that must take effect immediately, an asynchronously updated cache is insufficient. Depending on the boundary, use a transaction, serialised processing or an authoritative version check coordinated with acceptance; define what happens to requests already in progress.
For amount-based limits, checking remaining capacity and then incrementing usage in a separate step can admit two simultaneous requests. The authoritative owner needs an atomic reservation or equivalent concurrency control, with explicit release and settlement rules. Define whether the policy counts attempts, accepted payments, stakes or another measure before choosing the algorithm.
Keep account eligibility separate from transaction outcomes. A rejected eligibility check should not erase a valid historical posting, and an account change must not silently cancel a settlement already owed. The financial domain needs its own approved treatment of outstanding operations.
4. Make account transitions explicit and testable
For every command, specify the actor, previous state, guard conditions, new state, durable effects, emitted facts and failure response. Include an account or case version so conflicting updates can be detected. Use server-authorised transitions instead of letting clients submit an arbitrary target status.
Four transition cases worth reviewing
- Verification approval: a trusted result for the current case may move that case from pending to approved. Confirm the identity version and required evidence first. Recalculate eligible actions; leave closure, exclusion and unrelated restrictions intact.
- Self-exclusion activation: record its effective scope and time, then enforce the affected gambling restrictions across relevant entry points and sessions. Return success according to a defined enforcement guarantee; do not claim completion while required consumers remain unprotected.
- Limit change: validate the requested value and the applicable immediate-change or waiting-period policy. Preserve the current effective limit until the replacement is allowed to take effect. Show both values and the effective time.
- Account closure and possible reopening: record the reason and handle outstanding financial and operational work through approved processes. Reopening requires a new authorised transition and applicable checks; authentication or a KYC callback cannot perform it implicitly.
These are deliberately separate transitions, not a universal sequence of “registered → verified → active → closed”. Verification decisions and restrictions continue to change during the lifecycle. A diagram that only models successful onboarding leaves the harder operational behaviour undefined.
Store event time and receipt time separately when external messages can arrive late. Do not select the winning status solely by the latest arrival or a provider timestamp. Match the case, event identity and local version; investigate conflicting decisions through the authorised review process.
Duplicate detection also needs a policy. Normalised contact details or identity matches may identify a candidate, not prove that two accounts belong to the same person. Protect uniqueness rules with storage constraints where appropriate, route ambiguous matches to review and preserve provenance when linking records. Never merge wallets merely because profile fields match.
5. Enforce current permissions across sessions and staff tools
OWASP's authorisation guidance recommends denying access by default and checking permissions on every request. Apply those checks to the specific action, account and operator context, including service-to-service requests.
Keep security authentication and business eligibility separate. A session can remain valid for a permitted support interaction while gambling is prohibited. Conversely, a verified account does not make a stolen or revoked session acceptable. Enforce both decisions at the relevant resource.
Make revocation work beyond the browser
The OWASP session management guidance calls for server-enforced expiry and invalidation. Removing a browser cookie alone does not invalidate another copy of the session.
Define how logout, credential recovery, suspected compromise and administrative revocation affect all relevant sessions and refresh credentials. With self-contained tokens, removing a refresh token does not necessarily invalidate an access token already issued. Use a server-side session or revocation/version check where prompt revocation is required, and document the remaining validity window.
Do not rely on the next page load to enforce a changed gambling restriction. Test already open game sessions, mobile clients, direct APIs and provider callbacks. Identify which provider protocols can stop new actions and which outstanding results still require settlement.
Give staff narrower powers than the account API
- Separate responsibilities: distinguish viewing a profile, viewing identity evidence, changing account restrictions, reviewing KYC and authorising financial adjustments.
- Validate object scope: check the staff member's operator, brand and case permissions, not just a role name. Changing an account ID in a request must not expose another player's data.
- Record sensitive actions: retain the actor, reason, approval where required, previous and resulting state, policy version and case reference in a tamper-resistant audit trail.
- Protect recovery: verify ownership through an approved recovery path, rate-limit abuse and use additional authentication for sensitive changes. Support impersonation, if allowed, must have explicit scope and visible audit evidence.
Apply comparable controls to exports, batch tools and scheduled jobs. A carefully protected staff screen provides little assurance if an import script can overwrite restrictions without checking the same authority.
6. Design for provider failures, recovery and sensitive data
A provider timeout means the result may be unknown; it does not mean that verification failed or that sending another case is safe. Keep a durable case reference and reconcile by that reference before retrying an operation that may create a duplicate.
- Duplicate or replayed callback: identify the provider event and apply its permitted transition once. A retry should not create a second approval, notification or audit action.
- Out-of-order result: retain the evidence, verify case and data versions, and prevent an older result from replacing a newer authorised decision.
- Unmatched result: isolate it for investigation instead of attaching it to an account using a fuzzy name or email match.
- Provider unavailable: keep affected cases pending, show a truthful status and expose an owned review queue. Do not silently convert absence of evidence into permission.
- Local write succeeds but publication fails: use a durable publication mechanism, such as a transactional outbox, so downstream consumers can recover the committed change.
- State service or cache unavailable: specify action-specific failure behaviour. If required eligibility cannot be established, reject or defer that controlled action; define any permitted read-only and support paths separately.
Reconciliation should compare provider cases, local decisions and consumer processing positions. Prioritise missing restrictions, unresolved cases and mismatched identity versions; assign an owner and an escalation threshold. Queue length alone cannot reveal whether one serious discrepancy has been waiting too long.
Treat identity evidence as a separate sensitive asset. Restrict document access, encrypt storage and transport, avoid raw documents and tokens in logs, and use synthetic or appropriately redacted test data. Define retention and deletion by purpose and applicable obligations, including exceptions that require authorised retention.
Closing an account is not the same operation as deleting every record. Document what can be removed, what must remain, who authorises an exception and how deletion propagates to providers and backups under the agreed lifecycle. Conversely, an audit requirement should not become an excuse to keep every identity document indefinitely.
7. Deliver in slices and accept the design with evidence
Build small slices that exercise the real control boundary: register and identify an account; process one verification case; authorise one protected action; propagate one restriction; recover one failed integration. Include the staff workflow and audit evidence in each slice.
Before migration, map old identifiers, status meanings and ambiguous restrictions. A legacy “active” value does not establish current identity approval or absence of an exclusion. Reconcile records against authoritative sources, quarantine ambiguous cases and record how outstanding transactions will be handled.
Set operational measures with defined starting and ending events: age of unresolved verification cases, delay from restriction commitment to enforcement at each required boundary, mismatches found by reconciliation, session-revocation delay and unauthorised transition attempts. Define thresholds from the approved policy and operating capacity rather than inventing universal numbers.
Accept the design through representative failure and concurrency tests. For each test, capture the permitted and denied actions, final records, consumer state and audit trail. A successful onboarding demo does not establish that a restriction survives a late callback or a second device.
For the wider integration model, read How the Core Modules of an iGaming Platform Work Together. Pair this account design with Designing a Reliable Wallet and Transaction Ledger for iGaming and Building KYC and Player Verification Workflows for iGaming.
Related architecture and primary sources
Review staff operations in iGaming Back Office Architecture: Roles, Workflows and Auditability, and deployment boundaries in Modular iGaming Platform Architecture: Core Domains and Boundaries.
- OWASP: Authorization Cheat Sheet
- OWASP: Session Management Cheat Sheet
- Gambling Commission: LCCP condition 17.1.1 — customer identity verification
Acceptance scenarios
- Late verification after exclusion: submit a case, activate the applicable exclusion, then deliver approval twice. The case may update under its rules, but the exclusion remains and affected gambling actions are denied on every required channel.
- Changed identity data: change a material identity field while verification is pending, then deliver the old case result. It must not approve the new identity version; operations can see why reassessment or review is required.
- Concurrent limit use: send two valid requests whose combined amount exceeds remaining capacity. The approved accounting policy is respected without double reservation, and retries return the original outcome.
- Revocation and authorised recovery: revoke one of several sessions and attempt protected calls with its existing credentials. Access follows the documented revocation guarantee; a permitted recovery or funds-return path works without restoring gambling eligibility.
Is player account management the same as authentication?
No. Authentication establishes who is making a request and manages credentials and sessions. PAM manages the account lifecycle and connects the facts used for business eligibility. Verification, exclusions, limits and financial state have their own owners. A correct request needs an acceptable session and permission for the specific action; neither a successful login nor an approved identity check authorises every operation.
Should PAM be a microservice?
Not automatically. Begin with domain ownership, consistency needs, team capability and failure boundaries. A module inside the platform can enforce the same contracts as a separate service. Extraction is useful when independent ownership, deployment or isolation justifies network calls and operational cost. Before distributing eligibility checks, prove how restrictions, concurrent requests and unavailable dependencies will be handled.
Can a KYC provider set the account to active?
A provider can report evidence or a case outcome through an authenticated integration. The platform should map that result to the correct case and identity version, then evaluate its own approved eligibility policy. The response must not clear unrelated restrictions, reopen a closed account or authorise stale identity data. Missing or conflicting evidence needs an explicit pending or review path.
What happens to withdrawals when an account is restricted?
Define withdrawals, refunds and other funds-return processes separately from new gambling, using the operator's applicable obligations and approved procedures. Avoid a blanket account-state rule that blocks every action without a reasoned policy. Record why information or review is required, who owns the case and what may proceed. Relevant legal and compliance specialists must approve those rules; a generic technical design cannot determine every market's treatment.
Bring one real player journey, your current account and verification states, provider contracts, and the restrictions or recovery cases that are difficult to explain. SPINDO.TECH can help map ownership, resolve control gaps and define implementation steps with reviewable acceptance evidence.
Insights
Designing an iGaming Wallet: Make Every Balance Explainable
Design a wallet that can explain deposits, holds, stakes, payouts and corrections from durable records. Work through balanced postings, atomic spending decisions, replay-safe operations and reconciliation with concrete review criteria.
14 min read
iGaming Back Office: Permissions, Approvals and Audit Evidence
Design staff tools that make sensitive actions explainable: scoped permissions, independent approval, safe balance corrections, player timelines and protected audit records.
14 min read
Modular iGaming Architecture: Who Owns the Rule, Record and Recovery?
Design useful boundaries between player accounts, wallets, games, payments and bonuses. Follow a mixed-funded stake through a late reversal and test the contracts between modules.
14 min read