
- multi-brand
- tenant isolation
- platform architecture
- configuration
Multi-Brand iGaming: Share the Core, Define the Boundaries
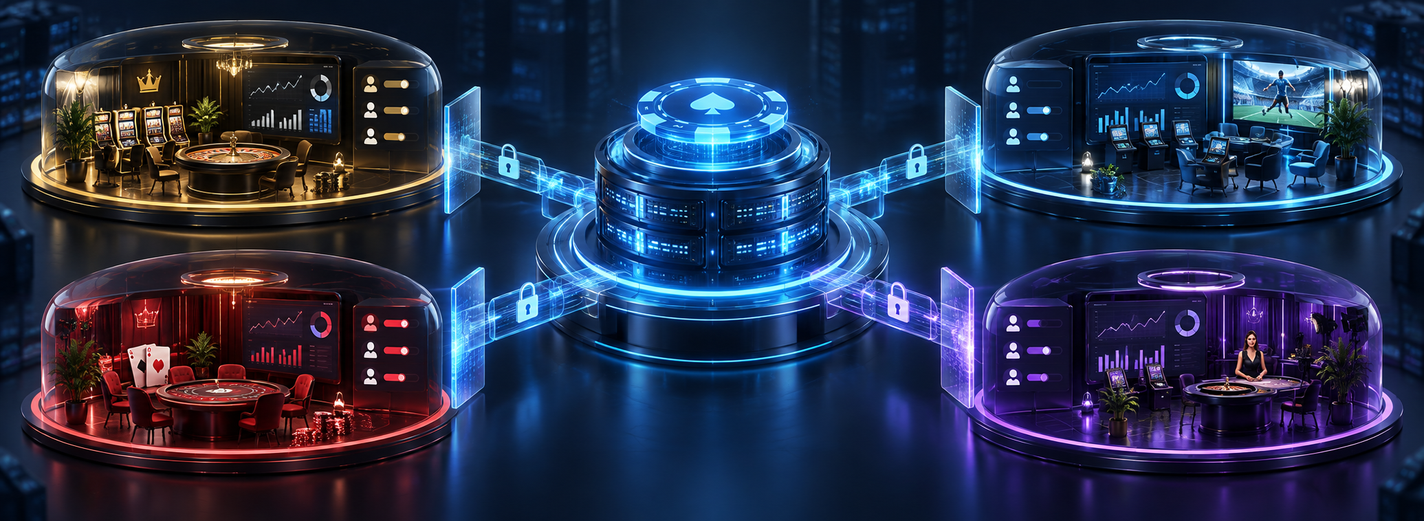
Design a shared iGaming platform with explicit brand, account, provider and operating boundaries. Test isolation through configuration changes, late callbacks and peak workloads.
Launching another brand on an existing iGaming platform appears simple when the work is described as a new theme, domain and game catalogue. The harder questions emerge when a support agent sees the wrong player, a configuration change reaches every brand or a delayed provider message credits the wrong wallet. Reusing software is valuable only when the resulting operation remains explainable.
This guide is for operators, product leaders and architects deciding how several brands should use a common platform. It distinguishes shared implementation from shared business authority and develops a review method for data, configuration, providers and operating capacity. The two-brand walkthrough is hypothetical; it assumes separate player wallets and provider merchant accounts, not a recommendation to combine balances or legal responsibilities.
Separate the brand, tenant and operating entity
Start with an explicit relationship map. A brand is a player-facing proposition. A tenant is the scope in which the platform controls resources and permissions. An operating entity is the party responsible for the actual business. A market, licence, environment and provider account add other dimensions. They need not have a one-to-one relationship.
One operator might run several brands inside one tenant while restricting staff by brand. A platform serving separate operators may need tenant isolation above brand scope. Write down which identity, account, wallet, restriction and reporting records belong at each level. A person recognised across brands does not automatically have a common gambling account or spendable balance. Conversely, a required group-wide restriction must not be defeated by treating every brand as unrelated.
The operator and qualified advisers must establish applicable market, contractual, player-protection and data-sharing requirements. Engineering should implement the approved scope rather than infer permission from common ownership. If cross-brand identity matching is authorised, define its purpose, access and effect; avoid exposing a complete portfolio profile to every support agent.
The platform capability overview helps locate the product surface. The domain-boundary guide addresses responsibility inside that surface. Here the additional question is which tenant or brand each decision may affect.
Choose the isolation model for each resource
Shared code does not require shared storage or a single deployment. Choose the boundary for each resource after defining what must be separated and which failure may affect another brand.
- Pooled resources: brands use common application or storage resources with enforced logical scope. This can simplify common updates and resource use, but requires dependable access boundaries and capacity controls.
- Dedicated resources: a tenant or brand gets selected databases, workers or a fuller environment. This can narrow certain failures and simplify some boundaries, while increasing provisioning, migration and operating work. Shared administration and upstream dependencies still need review.
- A mixed model: keep suitable capabilities common and dedicate the resources that need a stronger boundary. AWS describes this combination as a bridge isolation model; the choice can be made by resource rather than for the entire platform.
Record decisions as a list. For each area, specify the owner, scope, allowed sharing, enforcement point and evidence: account data and money records; provider credentials and routing; themes and catalogues; staff access and exports; reports; workers; backups. “Shared” should describe an implementation or approved read view, not an unspecified right to edit every brand.
If PostgreSQL is selected, row policies can add a data boundary. Its row-security documentation states that superusers and roles with BYPASSRLS bypass those policies; table owners normally do too. Test the deployed application role, not only the policy definition. This is a database-specific consideration, not a claim that every platform or this project uses PostgreSQL.
Carry verified context through every access path
A brand selector, hostname or request parameter can select a desired context; it cannot establish permission by itself. Bind the selection to a verified player, staff or service identity and the operation it is allowed to perform. Reject missing or conflicting scope on paths that require it.
OWASP’s multi-tenant security guidance distinguishes client-selected context from server-verified authority. Apply that distinction to player lookup, money commands and provider routing: access must agree with both the caller’s scope and the target record.
Trace that context beyond the web request. Identify which cache entries, documents, search results, reports and messages vary by brand or tenant, and review their access paths. Public reference data can be intentionally shared; a protected player export needs a different boundary. Reusing a database connection or worker must not reuse another request’s scope.
Give portfolio-wide staff access an explicit identity, purpose and permission set. The back-office overview helps define the work; the staff-permission and audit guide develops controlled actions. A cross-brand report does not grant cross-brand correction rights. Record the actor, affected scope, approval where required and committed outcome for sensitive changes.
Make configuration a controlled product release
Configuration is part of product behaviour. A colour palette and a withdrawal route should not share the same approval or failure policy. Separate presentation choices, commercial settings and rules that affect money, eligibility or account restrictions.
- Resolve explicitly: document the supported default and override levels, such as platform, tenant, brand and market. Show the effective result before publication. A missing provider credential or mandatory rule must not silently inherit an unsafe global value.
- Validate combinations: check supported currencies, provider accounts, permitted catalogues and dependent features together. A switch can expose a capability the surrounding workflow cannot support.
- Publish a version: keep the proposed change, difference, approver, activation point and recovery plan. Apply relevant cache invalidation and test the intended scope as well as unaffected brands.
- Preserve accepted terms: distinguish rules for new activity from evidence explaining work already accepted. Retain the relevant configuration or policy reference where the workflow needs it; do not rewrite history when a setting changes.
Prefer validated variation points over a code fork for every brand. A fork can make a brand-specific change appear inexpensive while making future fixes diverge. Equally, a configuration system should not become an unrestricted programming language. If brands require incompatible transaction rules or independent release obligations, revisit the domain or deployment boundary instead of stacking hidden exceptions.
Reverting a setting changes future behaviour under its agreed semantics. It does not reverse an accepted bet, complete a pending payment or remove the need to explain a decision taken under the earlier version.
Keep late provider work attached to its original scope
Consider brands North and South. In this example each has a separate player numbered 47 and its own provider merchant account. The provider contract defines operation numbers within each merchant account. Both accounts can therefore legitimately report operation 707 without referring to the same transaction.
North accepts a game operation using configuration version 12. Its record identifies North’s player and wallet, provider account, original request, operation meaning and relevant accepted terms. Later, North publishes version 13 with a different route for new activity. A delayed result for the earlier operation still belongs to the original North record.
- Authenticate the arrival: verify the provider path and its permitted account scope. A brand name in the payload is not sufficient authority.
- Resolve against accepted work: use the original provider account and operation references to find the owned record. Do not choose South’s wallet or North’s new route from the current default.
- Handle identity under the contract: the two merchant-scoped 707 operations must remain distinct. A repeated North operation has one allowed financial effect; conflicting parameters require investigation or rejection. Do not add brand to a deduplication key blindly when a different contract defines a genuinely global operation.
- Keep recovery explainable: preserve arrival evidence and the result. Unknown or conflicting references go to an owned exception process rather than a guessed wallet. Staff must see the correct scope without acquiring permission to repair another brand.
Use this walkthrough for deposits, game results and betting settlement, adapting the state rules to each product. Existing accepted obligations still need a recovery path when new activity is disabled. Recovering an earlier financial obligation is not permission for new play: current account restrictions and approved settlement rules still apply. For queue topology, Microsoft’s multitenant messaging guidance compares shared and dedicated infrastructure; a shared broker alone does not establish the application’s ownership rules.
Protect capacity and recovery across the portfolio
A brand can be isolated for data and still disrupt another brand’s service. A promotion may consume shared workers, a report may occupy database connections, and several brands may use the same supplier quota. Separate application replicas do not isolate a shared financial database or upstream merchant limit.
Measure demand and unfinished work by the scope that matters: tenant, brand, workflow and provider account. Agree capacity allocation, service-wide limits and the circumstances for dedicated workers or other resources. Test one brand’s burst while another performs its essential journeys. Preserve capacity for accepted monetary work instead of letting optional exports dominate recovery. The peak-load guide develops admission and completion planning.
State the actual release independence. A feature enabled for one brand can still rely on a migration applied to the shared database. Review compatibility with other brands and their in-flight work. Dedicated environments also require automated provisioning, patching, monitoring and evidence collection; otherwise their isolation can come with unnoticed operational drift.
Rehearse recovery at the chosen boundary. If one brand needs restoration in a shared database, a whole-database rollback could overwrite later work for other brands. Agree a recovery method that preserves their records, and reconcile restored money data with accepted external operations. Include provider credentials, audit evidence, exports and unfinished work in offboarding; ending new traffic does not settle existing obligations.
Prove the next brand before opening access
Choose one workflow to exercise in two brands so that it exposes the important boundaries. Test it with permitted actors, forbidden scope changes, delayed work and a configuration release. Show which platform capability is shared, which record is owned and which approved setting changes the behaviour.
Acceptance should include positive and negative cases. The intended player or staff member must complete allowed work; another brand’s identifier must not expand access. Run the same checks through ordinary requests, provider callbacks, reports, exports and background execution where those paths exist. Test explicit portfolio-wide permissions separately from ordinary brand access.
Keep the decision package usable: the operator/tenant/brand map, resource choices, effective configuration, provider-account mapping, permission rules, failure scenarios and operating owners. Open conditions belong in the release decision, not in an undocumented promise of “independent brands”. The four review checks below summarise evidence the receiving team should be able to reproduce.
For sequencing and launch decisions, continue with planning a new iGaming product. To specify a review and receive usable decisions, use discovery and architecture sprint outputs. When a brand includes betting, the sportsbook architecture guide explains ticket, wallet and settlement states that the brand boundary must preserve.
- Scope and access: demonstrate permitted same-brand work, denied cross-brand reads and writes, and explicitly approved portfolio operations across actual access paths.
- Configuration: show the effective version, approval and activation scope; prove that another brand is unaffected and accepted work remains explainable.
- Provider recovery: replay the merchant-scoped example, change current routing and resolve delayed or conflicting results against the original owned records.
- Operating isolation: run a brand-specific burst, inspect other brands’ essential journeys and rehearse recovery without overwriting their accepted work.
Does every brand need a separate database?
No. Choose boundaries from the required data access, recovery, operating and contractual conditions. Shared storage needs enforceable scope and evidence; dedicated storage adds its own provisioning, administration and migration work. Shared credentials or unrestricted administrative paths can undermine either design.
Can players and balances be shared across brands?
Only under an explicitly approved product and operating model. Identity matching, account membership, restrictions and monetary ownership are separate decisions. Sharing code or a parent company does not establish permission to combine balances or disclose player data. Confirm the applicable requirements with responsible specialists.
Are different themes enough for a multi-brand platform?
They address presentation, not the complete operating boundary. Examine account scope, provider contracts, wallet ownership, staff rights, reports, configuration, recovery and capacity. Some capabilities may be intentionally common; make the permission and responsibility for that sharing explicit.
When should a brand move to dedicated resources?
Consider it when required recovery, release independence, access separation or capacity cannot be achieved reliably in the current shared boundary. Identify the actual bottleneck or risk first: separating workers will not isolate a shared provider quota. Include migration and ongoing operation in the decision.
Bring your operator and brand map, provider account structure and one workflow that must remain isolated. We can assess the shared platform, configuration and recovery boundaries and define evidence for a bounded architecture or implementation stage.
Insights
How to Plan the Launch of a New iGaming Product
A practical launch plan for founders and delivery teams: define a viable MVP, qualify suppliers, budget for dependencies, test money flows, and make an evidence-based go/no-go decision.
14 min read
What an iGaming Discovery and Architecture Sprint Should Deliver
Assess a discovery sprint through usable evidence, architecture decisions, provider dependencies and a conditional delivery plan your team can act on.
14 min read
Sportsbook Platform Architecture: Bets, Wallets and Settlement
Design a sportsbook around explicit bet, funding and settlement states. Trace a lost provider response, protect wallet commitments and recover financial corrections.
14 min read